AI Red Teaming: What CAIOs Need to Know About Proactive AI Threat Simulation
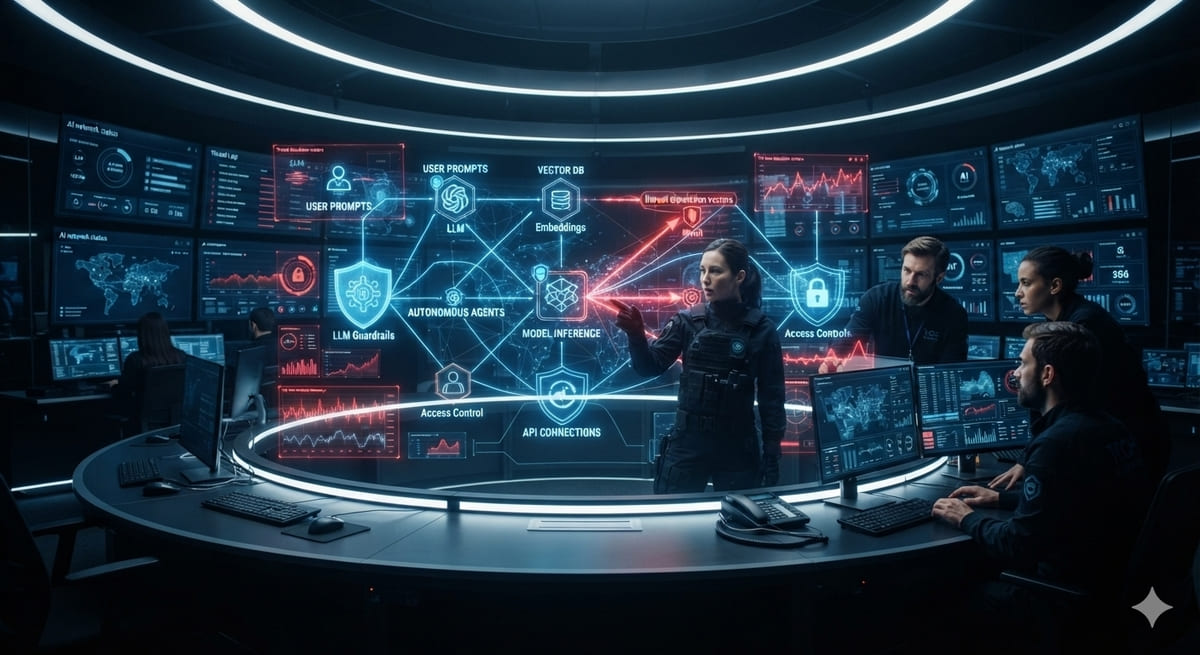
AI red teaming is a structured, continuous process of simulating attacks against Large Language Models, RAG pipelines, and agentic workflows to uncover security and safety vulnerabilities. Unlike traditional pen-testing that targets static code, AI red teaming stresses probabilistic reasoning to prevent prompt injections, data poisoning, and unauthorized tool calls before exploit. For Chief AI Officers, institutionalizing red teaming is an essential operational pillar for regulatory compliance, risk mitigation, and enterprise resilience.
RMN Digital CAIO Hub
New Delhi | November 3, 2026
Editor’s Note: This article is part of the RMN Digital CAIO Hub, an executive intelligence platform providing blueprints, frameworks, and operational strategies for Chief AI Officers and enterprise technology leaders. Explore the full collection of insights and strategic frameworks at the RMN Digital CAIO Hub.
As enterprises shift from deterministic IT workflows to probabilistic artificial intelligence platforms, traditional cybersecurity mechanisms are proving inadequate. Standard vulnerability scanners, static application security testing (SAST), and network firewalls were built to inspect code syntax, open ports, and API payloads. They cannot detect subtle prompt injections, evaluate semantic drift, or stop an autonomous AI agent from executing unauthorized tool parameters.
AI Red Teaming is the structured, proactive process of simulating real-world adversarial attacks against artificial intelligence systems—including foundational Large Language Models (LLMs), fine-tuned domain models, Retrieval-Augmented Generation (RAG) pipelines, and multi-agent frameworks.
The objective is to surface security vulnerabilities, safety flaws, and edge-case operational failures before malicious actors exploit them in production environments. For Chief AI Officers (CAIOs), AI red teaming is no longer an optional pre-launch check. It is a fundamental operational requirement for risk management, regulatory compliance (including the EU AI Act and NIST AI RMF), and enterprise resilience.
Also Read and Subscribe to:
[ Technophile | Tech Insights LinkedIn Newsletter ]
The AI Attack Surface: Where Legacy Security Fails – Traditional penetration testing assesses whether an attacker can exploit software bugs to gain unauthorized network access. In contrast, AI red teaming probes the probabilistic behavior and contextual reasoning of deployed AI stacks. Adversaries manipulate how models interpret natural language, query vector stores, and invoke downstream enterprise tools.
+-------------------------------------------------------------------------+
|                        ENTERPRISE AI ATTACK SURFACE                     |
+-------------------------------------------------------------------------+
|  [ User Interface ]  ---> Direct Prompt Injections & Jailbreaks          |
|  [ RAG Pipeline ]   ---> Data Poisoning & Unauthorized Vector Retrieval |
|  [ Agentic Tools ]  ---> Privilege Escalation & Unsafe API Execution   |
|  [ Output Layer ]   ---> Cross-Tenant Data Leakage & System Prompt Theft|
+-------------------------------------------------------------------------+
Primary Vulnerability Vectors (OWASP LLM Top 10 Alignment)
| Vulnerability Vector | Operational Mechanism | Enterprise Impact |
| Direct Prompt Injection & Jailbreaking | Overriding system instructions using deceptive phrasing, multi-turn escalation, or encoded tokens. | Safety policy bypass, unapproved business commitments, brand risk. |
| Indirect Prompt Injection | Ingesting hidden adversarial instructions embedded within third-party PDFs, web pages, or CRM records. | Hijacking model logic through untrusted external data sources. |
| RAG Poisoning & Retrieval Abuse | Manipulating vector database embeddings or injecting unauthorized content into enterprise memory. | Exposing cross-tenant PII, financial leaks, corrupting knowledge stores. |
| Agentic Tool & Excessive Agency | Tricking autonomous agents into invoking connected APIs with harmful parameters. | Unauthorized financial transfers, data deletion, privilege escalation. |
| System Prompt & IP Theft | Adversarial extraction queries designed to reveal internal system prompts and guardrails. | Exposure of competitive logic, system architecture, and trade secrets. |
Structuring an Enterprise AI Red Teaming Methodology: A robust enterprise red teaming engagement avoids unstructured, manual “jailbreak poking.” It follows a systematic, multi-tiered framework executed across the full software delivery lifecycle.
+-------------------+     +-------------------------+     +------------------------+     +----------------------+
| 1. Threat Modeling | --> | 2. Surface Enumeration  | --> | 3. Adversarial Testing | --> | 4. Risk Scoring &    |
|    & Scope Mapping |     |    (Prompts, RAG, APIs)  |     |    (Automated + Manual) |     |    Remediation       |
+-------------------+     +-------------------------+     +------------------------+     +----------------------+
1. Threat Modeling & Scope Mapping
Red teams must map the complete system architecture—base models, system prompts, retrieval indexes, connected APIs, and user access levels.
- Key Audit Question: What data sources, internal databases, and execution channels can this AI system access?
2. Hybrid Adversarial Testing
Effective AI red teaming combines continuous automated testing with creative human evaluation.
- Automated Red Teaming: Automated harnesses execute synthetic attack suites against CI/CD pipelines to detect regressions across prompt changes and model updates.
- Manual Red Teaming: Experienced security researchers craft multi-turn, domain-specific exploits that automated frameworks cannot infer.
3. Risk-Tiered Scoring & Remediation
CVSS metrics struggle to score probabilistic vulnerabilities. Red teaming findings should be evaluated by measuring Exploitability vs. Downstream Impact.
Executive Note: A model generating off-brand text is a low-severity operational issue. A prompt injection that tricks a customer-facing support agent into executing a database deletion script is a critical-severity operational breach.
4 Strategic Mandates for Chief AI Officers
- Shift from One-Off Audits to Continuous CI/CD Red Teaming: AI applications change continuously through vector updates, prompt tweaks, and model re-indexing. Embed automated red teaming gates directly into delivery pipelines.
- Enforce Defense-in-Depth Architecture: Never rely solely on system prompts for system security. Implement input filtering, output guardrail layers, vector database role-based access controls (RBAC), and strict tool permissions.
- Bridge SecOps and AI Engineering: Align machine learning developers with enterprise security operations to ensure threat models cover both software infrastructure and transformer-level logic.
- Maintain Audit-Ready Compliance Artifacts: Regulatory frameworks (such as NIST AI RMF and ISO/IEC 42001) demand documented risk tracking and stress testing logs. Structured red team reports provide crucial evidence during third-party security audits.
Summary for Executive Leadership
Probabilistic reasoning offers immense operational flexibility, but it introduces novel security challenges. CAIOs must establish structured AI red teaming programs to identify systemic boundaries, protect proprietary IP, and maintain customer trust across all autonomous deployments.